
Kubernetes Red Team Certification
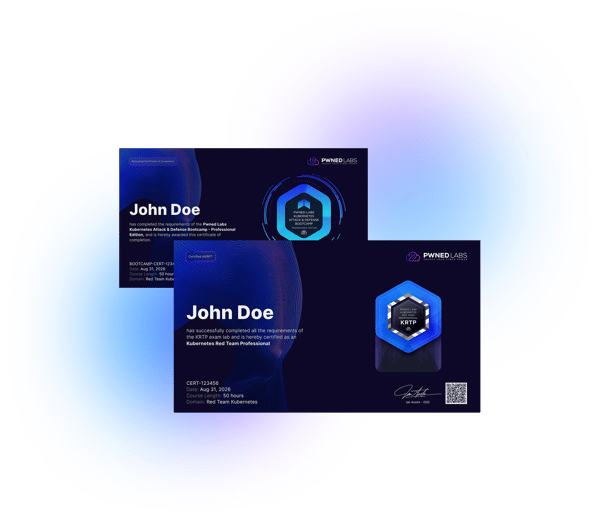
Kubernetes Red Team Certification at a glance
- Full name: Kubernetes Red Team Professional (KRTP)
- Format: Hands-on, assessed in a live Kubernetes cluster
- Focus: RBAC escalation, container escape, service account tokens to cloud credentials
- Level: Professional
- Prerequisites: a general security foundation (no prior Kubernetes experience required)
- Delivered via: the Kubernetes Attack and Defense bootcamp
The Kubernetes Red Team Professional (KRTP) is a hands-on Kubernetes red team certification, earned through the Kubernetes Attack and Defense bootcamp, an on-demand Pwned Labs program that goes deep on modern attack chains and the detections that catch them, then certifies you hands-on.
Kubernetes is often the platform red teamers understand least, which is exactly why attackers target it. The API server sits in front of a database, RBAC decides who can do what, and service account tokens and node identity quietly bridge the cluster to the cloud account behind it. Those mechanics create attack paths that go unnoticed. A Kubernetes red team certification should prove you can find and exploit them in a live cluster. The Kubernetes Red Team Professional (KRTP) is built to do that, hands-on.
What the KRTP certification proves
KRTP is a practical Kubernetes red team certification. There is no multiple choice section. You are assessed inside a live Kubernetes cluster with realistic misconfigurations and telemetry, and you have to enumerate the cluster, gain a foothold from a low-privilege pod, escalate to cluster-admin, escape to the node, and pivot into the cloud account to reach the objective. Passing means you demonstrated real tradecraft against real Kubernetes infrastructure, which is a credential an employer can trust.
Who this certification is for
KRTP fits penetration testers moving into cloud native, red teamers who need Kubernetes depth, and platform and cloud security engineers who want offensive understanding to strengthen their defenses. You do not need prior Kubernetes experience. The Kubernetes Attack and Defense bootcamp that leads into KRTP starts from fundamentals in minikube and progresses into RBAC escalation, container escape, and cloud identity abuse across EKS, GKE, and AKS, so a strong general security background is enough to start.
What you learn on the path to KRTP
The curriculum tracks how Kubernetes clusters are actually compromised rather than listing platform features. Core areas include:
- Cluster enumeration from an unauthenticated external position and from a low-privilege pod foothold.
- Analyzing service account tokens and RBAC to find verbs equivalent to cluster-admin, then escalating through RBAC misconfigurations.
- Escaping the container to the host node and dumping every secret in the cluster.
- Reaching the Instance Metadata Service from a pod and abusing IRSA, EKS Pod Identity, Fargate task credentials, and workload identity federation across EKS, GKE, and AKS.
- Establishing in-cluster and cloud-side persistence, weaponizing admission webhooks, and reading Kubernetes audit logs so you understand what defenders record while you operate.
Because the labs run in production-like clusters, you build the blue team awareness that distinguishes a Kubernetes red teamer from someone who only ran a script.
KRTP compared to other Kubernetes security certifications
The Certified Kubernetes Security Specialist (CKS) is a defensive, configuration-focused exam. It validates that you can harden and operate a secure cluster and is valuable for platform and engineering roles, but it does not ask you to attack one. Other offensive exams prove general penetration testing skill while covering little of the RBAC, container escape, and node identity abuse that defines Kubernetes compromise. KRTP fills that gap with a fully hands-on, offense-focused assessment specific to Kubernetes and the cloud accounts behind it.
How the KRTP exam works
The certification is assessed in a live Kubernetes cluster, not a simulation. You are given objectives and a time window and must accomplish them with real tradecraft against real services that are logging your activity. There is no memorization component. You reach the objectives or you do not, which makes the credential difficult to fake and easy for an employer to verify.
Inside the KRTP exam environment
The exam is a single realistic scenario, not a question bank. You get 24 hours and an entry point into a live Kubernetes cluster and the cloud account behind it, then build a complete exploitation chain from that foothold to the flag. The cluster, the misconfigurations, and the audit logging are all real.
It is self-contained and unproctored, so there is nothing external to bring and no screen recording. Because it is a chain rather than isolated tasks, partial knowledge shows, and there is no pentest report to write. You capture the flag or you do not, which makes the credential easy for a hiring manager to read.
Preparing for the KRTP exam
You do not need prior Kubernetes experience to start. What you do need is comfort on the Linux command line, the ability to read YAML and JSON, and a general security foundation. Familiarity with containers helps, but the bootcamp opens with fundamentals in minikube before moving into the advanced material, so the ramp is built into the path.
Frequently asked questions
What does KRTP stand for?
KRTP stands for Kubernetes Red Team Professional. It is the hands-on certification earned through the Kubernetes Attack and Defense bootcamp at Pwned Labs.
Is KRTP a hands-on certification?
Yes. KRTP is assessed in a live Kubernetes cluster with realistic misconfigurations and telemetry. There is no multiple choice component.
Do I need Kubernetes experience before starting?
No prior Kubernetes experience is required. The bootcamp starts with fundamentals in minikube and builds toward RBAC escalation, container escape, and cloud identity abuse. A general security foundation is enough.
How is KRTP different from the Certified Kubernetes Security Specialist (CKS)?
CKS focuses on hardening and operating clusters securely. KRTP is an offensive, fully practical certification earned by operating in a live cluster. They serve different, complementary goals.
Does KRTP cover managed Kubernetes on AWS, Azure, and GCP?
Yes. The curriculum covers minikube fundamentals and then EKS, GKE, and AKS, including turning a service account token into a cloud credential on each provider.
What roles does KRTP support?
Cloud and cloud native penetration tester, red teamer, and platform or cloud security engineer roles where proving offensive Kubernetes capability matters.
What practitioners say.
Dani Schoeffmann
Security Consultant, Pen Test Partners
"I found the Pwned Labs bootcamps well structured and strongly focused on practical application, with clear background on how and why cloud services behave the way they do and how common attack paths become possible. The team demonstrates both sides by walking through attacks and the corresponding defenses, backed by hands-on labs that build confidence using built-in and third-party tools to identify and block threats. The red-team labs are hands-on and challenge-driven, with clear walkthroughs that explain each step and the underlying logic. I’ve seen several of these techniques in real engagements, and the bootcamp helped me develop a repeatable methodology for cloud breach assessments and deliver more tailored mitigation recommendations."
Matt Pardo
Senior Application Security Engineer, Fortune 500 company
"I’ve worked in security for more than 15 years, and every step up came from taking courses and putting the lessons into practice. I’ve attended many trainings over the years, and Pwned Labs’ bootcamps and labs are among the best I’ve experienced. When you factor in how affordable they are, they easily sit at the top of my list. As a highly technical person, I get the most value from structured, hands-on education where theory is immediately reinforced through labs. Having lifetime access to recordings, materials, and training environments means you can repeat the practice as often as needed, which is invaluable. If you’re interested in getting into cloud security, sign up for Pwned Labs.”