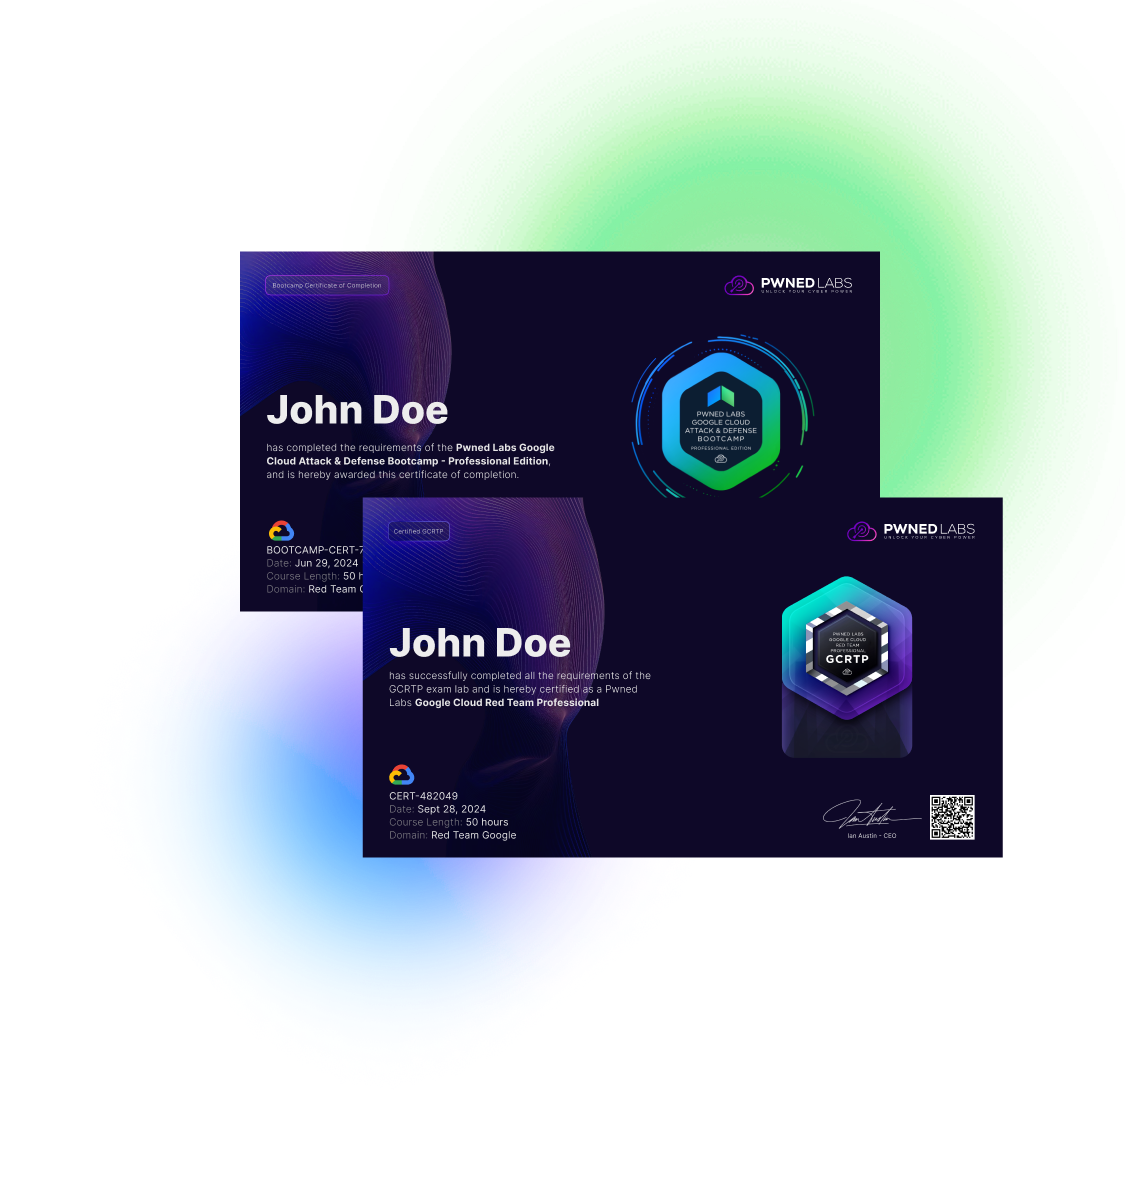
ON-DEMAND

Pwned Labs Google Cloud Attack & Defense Bootcamp - Professional Edition

GCRTP stands for Google Cloud Red Team Professional.

Hands-on Google Cloud attack and defense training focused on real-world attack paths across GCP and Google Workspace.


Ideal for: Penetration testers, security consultants, cloud red teamers, purple teamers, cloud security engineers validating GCP controls, and practitioners aspiring to these roles.


Designed for modern identity-driven Google Cloud environments, teaching operators to execute the tradecraft and evaluate agentic-assisted workflows end-to-end.


Already registered? Access here

Pwned Labs Google Cloud Attack & Defense Bootcamp - Professional Edition Overview

GCRTP_

Google Cloud is everywhere!

This on-demand bootcamp and structured learning path teaches practical techniques for attacking and defending GCP and Google Workspace environments. You will work through identity-driven attack paths across GCP and Google Workspace using techniques observed in active intrusions.

After completing the bootcamp and associated learning path, you will validate your skills in a fully hands-on, unproctored exam that requires completing an end-to-end exploitation chain.

The exam environment is dynamic, with scenarios changing regularly to reflect real-world Google Cloud intrusions and ensure certification credibility.


google_cloud2

Prerequisites and key learning outcomes

You should be comfortable using the Windows or Linux command line. Prior GCP experience is helpful but not required.

The GCRTP is the GCP and Workspace-focused track among the Pwned Labs cloud pentesting certifications.

After completing the bootcamp and passing the exam, you will demonstrate proficiency in:

  • Core GCP and Google Workspace security concepts
  • Identity-driven initial access and lateral movement in GCP
  • Auditing and exploiting misconfigured IAM permissions
  • Attacking and defending Google Workspace environments
  • Hands-on purple teaming against realistic attack scenarios
  • Investigating incidents using Google Cloud logging and security tools
  • Detecting and responding to real-world GCP attack paths
  • Attack and defend a broad range of GCP SaaS, IaaS, and PaaS services, including VMs, storage, CI/CD, and application services
google_cloud_pathway-1-1

What you get

You get ongoing access to the full GCP and Google Workspace security curriculum, organized into four pillars that align to the four sessions. Each pillar includes its own learning path so you can hit the ground running before the session starts.

  • Lifetime access to the latest session recordings, updated slides and command guides, bootcamp labs, and all future course updates
  • 45 days of Academy lab access for the learning paths tied to each session, starting from when you redeem your voucher rather than from purchase, with no deadline to claim and extendable with subscription
  • Direct preparation for the GCRTP certification exam
    More information on the bootcamp, learning paths, and the GCRTP exam is available on the
     GCRTP FAQ page.
apt-1

Focus on trending techniques and tradecraft

The Pwned Labs Google Cloud Attack & Defense Bootcamp, Professional Edition focuses on techniques used by real-world threat actors, including TRIPLESTRENGTH. Labs simulate realistic enterprise environments and active users across GCP and Google Workspace.

You will learn how to:

  • Identify and replicate tradecraft from recent cloud breaches
  • Execute attacks across identity, workloads, and CI/CD systems
  • Evict attackers and rotate or reset compromised credentials
Course syllabus

4 sessions13 hands-on bootcamp labs50+ hours of contentAligned Academy learning paths24-hour hands-on exam2 exam attempts$399

The Pwned Labs Google Cloud Attack & Defense Bootcamp (GCRTP) is a hands-on, on-demand red team course for Google Cloud and Google Workspace. Across four sessions you work identity-driven attack paths through GCP IAM, service accounts, and Workspace, then defend each one, before validating your skills in a 24-hour, fully hands-on exam.

Session 1: Getting initial access to Google Cloud

  • GCP and Google Workspace overview, and the gcloud CLI hands-on
  • External reconnaissance and identifying valid users and credentials
  • Identifying and protecting against password spraying
  • Leveraging exposed resources and harvesting secrets from code repositories
  • Bypassing the perimeter with phishing

Session 2: Attacking Google Workspace and IAM

  • GCP IAM overview and getting situational awareness
  • Service account lateral movement through token impersonation
  • Leveraging users and groups for access
  • Google Workspace post-exploitation, OAuth tokens, and data exfiltration
  • Google Workspace logging and detection

Session 3: Attacking and defending GCP resources

  • Identifying resources and effective resource permissions
  • Harvesting secrets from Secret Manager
  • Attacking and defending Compute Engine instances
  • Stealing Cloud Build service-account tokens and attacking Artifact Registry
  • Attacking Cloud Run and securing applications with Identity-Aware Proxy (IAP)

Session 4: Purple and blue teaming in GCP

  • Managing risk with Security Command Center (SCC)
  • Hunting threats with Cloud Logging, Logs Explorer, and Log Analytics
  • Trapping intruders with honey tokens and auditing access with Policy Analyzer
  • Installable Apps Script trigger lateral movement
  • Performing security assessments with Prowler, plus exam prep and a capstone CTF

Related concepts in our Security A-Z glossary: cloud IAM privilege escalation, cloud misconfiguration, cloud detection engineering, attack path analysis, and cloud incident response.

Meet the team

Our instructors are on hand in Discord to help whenever you need it.

matt_watkins-1-1

Matt Watkins has over a decade of experience in offensive and defensive security, spanning big tech, startups, and leading vendors, with a specialization in cloud security-particularly GCP.

He brings deep expertise in building and securing operations at scale, combining hands-on technical skills with a talent for breaking down complex topics to help teams understand both the "what" and the "why" behind modern security practices.

He brings an attacker-informed mindset to cloud defense, focusing on practical detection engineering, threat emulation, and real-world security operations in GCP environments.

Ian_Austin

Ian Austin is a security researcher and educator with a career spanning over 20 years in technical, security and leadership roles for global enterprises.

Ian was Head of Content at Hack The Box, a leading online platform for cybersecurity training and assessment. He also participated in the Green Team of Locked Shields, a NATO cyber defense exercise, contributing to the design and execution of realistic scenarios.

He is the founder of Pwned Labs, providing gamified and immersive cloud security labs for red and blue teams.

Informed by research

ayush-2

Pwned Labs bootcamps are shaped by ongoing research conducted both in-house and across the broader security community.

Ayush Singh develops tooling and tradecraft for GCP and Google Workspace, focused on offensive enumeration and analysis that directly informs course content.
raincloud-3

How it works

Start immediately with on-demand access. Work through the learning path and labs at your own pace. Your purchase includes 45 days of lab access and two GCRTP exam attempts. The 45 days begins when you redeem your voucher rather than at purchase, and there is no deadline to claim it. Lab access is extendable with subscription. Support is available via Discord.
What security teams say

“The AWS, Azure, and GCP bootcamps helped me get up to speed quickly on how real cloud environments are built and where they tend to break from a security standpoint. They were perfectly structured, with real-world examples. I’m now able to run cloud pentests more confidently and quickly spot meaningful vulnerabilities in customers’ cloud infrastructure.”

Sebas Guerrero, Senior Security Consultant, Bishop Fox

“The Pwned Labs bootcamps are well structured and strongly focused on practical application, with clear background on how and why cloud services behave the way they do. The team walks through attacks and the corresponding defenses, backed by hands-on labs. I’ve seen several of these techniques in real engagements.”

Dani Schoeffmann, Security Consultant, Pen Test Partners


Purchase options


Each bootcamp purchase includes two attempts at the GCRTP exam. Additional re-attempts can be purchased separately.

Bootcamp registration is required to attempt the exam.

Bulk and team purchases are available.


gcrtp_pricing-3
exam_reattempt-2

Ask your employer to fund GCRTP


Need employer funding approval? Use our ready-made employer funding request to outline the value of the Pwned Labs Google Cloud Attack & Defense Bootcamp - Professional Edition and the GCRTP certification.

Prefer to self-fund? You can enroll immediately.

Frequently asked questions

What is the GCRTP bootcamp?

The Pwned Labs Google Cloud Attack & Defense Bootcamp (GCRTP) is a hands-on, on-demand course covering Google Cloud and Google Workspace attack and defense. It teaches identity-driven attack paths across GCP IAM, service accounts, and Workspace, then certifies you through the Google Cloud Red Team Professional exam.

What does GCRTP stand for?

GCRTP stands for Google Cloud Red Team Professional. It is the hands-on certification earned by completing the bootcamp and passing the exam.

Do I need GCP experience to take the GCRTP?

No. You should be comfortable with the Windows or Linux command line. Familiarity with GCP is helpful but not required, and all the material you need to pass the exam is provided in the bootcamp and its structured learning paths.

How long is the GCRTP exam and is it proctored?

Once started you have 24 hours to complete an end-to-end exploitation chain from a provided entry point to capture the flag. The exam is fully hands-on, unproctored, and does not require a pentest report.

What tools and techniques does the GCRTP cover?

The bootcamp covers gcloud enumeration, service account impersonation and lateral movement, Google Workspace post-exploitation, Cloud Build token theft, Compute Engine and Cloud Run attacks, and defensive tooling including Security Command Center, Cloud Logging, Policy Analyzer, and Prowler.

Does the GCRTP certificate expire?

No. Once awarded, the GCRTP certificate does not expire or require renewal. Your registration includes two exam attempts, and exam attempts do not expire.

Which real-world threat actors does the GCRTP model?

Labs draw on techniques used by real-world threat actors, including TRIPLESTRENGTH, which targets cloud environments for cryptojacking and ransomware, across GCP and Google Workspace.


Got any Questions? Get in touch