
Overview
PromptStorm is an immersive blue team cyber range in the SkyFall Enterprise collection, built to put real incident response capability to the test in AWS environments that lean on AI and LLM workflows.
Defenders work a multi-stage breach: attackers pick apart weaknesses in AI workflows and cloud identity controls, escalate privileges, dial down visibility, and quietly monetize the environment with covert crypto-mining spread across several AWS regions. There is no traditional malware to find: long-term access rides on legitimate AWS automation and durable services instead, so responders have to reconstruct the intrusion end to end and carry the full response lifecycle through without knocking over production.
It complements the Pwned Labs AI security training, giving red teamers a defender’s view of how AI-enabled attacks are detected, and defenders a hacker’s mindset.
The PromptStorm range overview covers the scenario, the skills needed and the real-world context before you start.
The scenario
An AI-enabled AWS environment starts throwing off quiet signs that something is wrong.
- Cloud costs begin to rise without a clear cause
- Logs contain unexpected content
- Access patterns no longer align with intended behavior
- Audit visibility degrades at a critical moment
Underneath it is an active breach that has reached into identity, automation, and observability all at once. The job is to work out what is happening, take back control, and drive the incident to resolution without destabilizing production systems.
Investigation and response flow
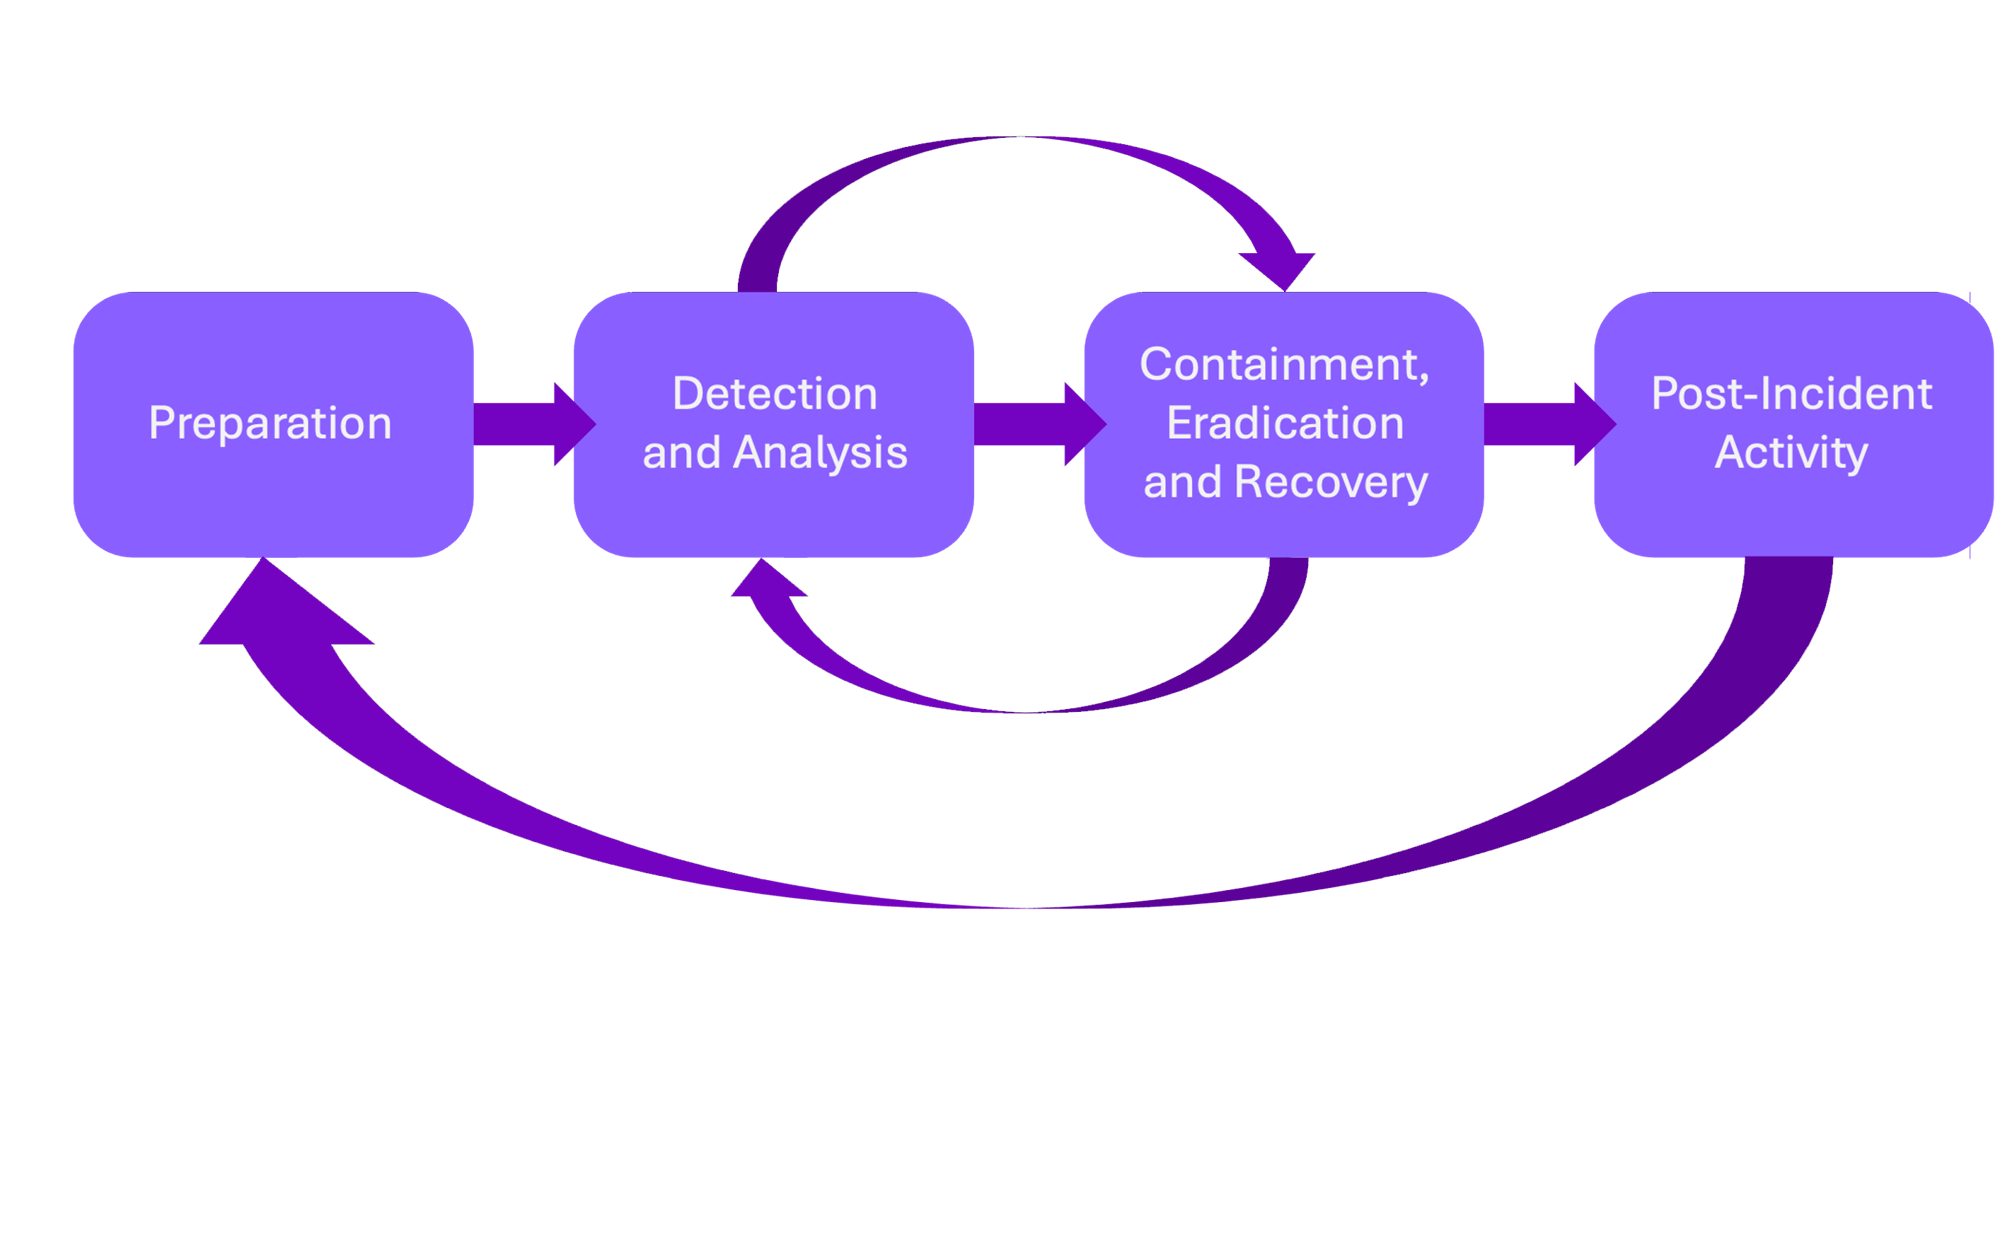
Nine challenges of mixed difficulty that walk through the incident response lifecycle.
PromptStorm runs the whole arc: early signal recognition, containment, remediation and recovery. Players handle a realistic breach and crypto-mining attack under live conditions, the kind of practice that keeps defenders cyber ready when a real one lands. Every challenge maps to an actual investigation or response decision point, and you advance on evidence: correlate what you are seeing, confirm what happened, restore visibility where it has been lost, and apply the corrective action that fits the moment.
What PromptStorm is designed to test
PromptStorm puts blue team judgment to the test under realistic conditions.
- Investigating AI-related security failures
- Tracing identity abuse across cloud services
- Operating with incomplete or degraded logging
- Distinguishing operational noise from adversary activity
- Making containment decisions under pressure
- Driving remediation and recovery without collateral damage
The test is in the investigation and the response calls, not in executing a fixed sequence of actions.
The Environment
Players operate inside a realistic AWS environment matched to the scenario, with:
- Optional custom SIEM integrations available on request
- Multiple AWS regions in use
- Identity and permissions that reflect real abuse paths
- Searchable OpenSearch logs and prebuilt dashboards
- Deliberately degraded audit visibility at key stages
- Active infrastructure impacted by attacker activity
The attack patterns and abuse paths in this environment follow tradecraft documented in Permiso Security’s research into the GUI-Vil threat actor.
Collaboration with threat researchers
Pwned Labs built PromptStorm in collaboration with Permiso Security, whose real-world research into cloud and LLM abuse shaped both the PromptPwn attack chain and the defensive challenges in this range.
Particular thanks go to Abian Morina and Andi Ahmeti from Permiso's P0 Labs team. Their work in cloud identity threat detection, privilege escalation, and detection engineering runs right through the range, including the LLM-driven policy manipulation and the crypto-mining persistence techniques.
What they contributed shows how modern cloud attacks actually play out, and gives defenders hands-on time with tradecraft they are running into more and more in live environments.
If you want to work the offensive side of these AI and LLM attack paths in depth, the AI Systems Attack and Defense Bootcamp, Professional Edition (AISRTP) covers prompt injection, RAG and embedding poisoning, tool and agent abuse, and MCP and CI/CD agent attack paths against LLM-backed and agentic applications.